Building sustainable digital resilience, beyond DORA compliance
In today’s financial ecosystem, operational resilience is no longer just an IT concern. Cyberattacks, technology failures, cloud dependencies and third-party service disruptions have become board-level risks that can directly impact business continuity, customer trust and regulatory compliance.
To address these challenges, the European Union introduced the Digital Operational Resilience Act (DORA), applicable since 17 January 2025, establishing a single and harmonised framework for managing digital operational resilience across the financial sector. DORA requires financial entities to not only protect themselves against ICT disruptions and cyber threats, but also to demonstrate their ability to withstand, respond to, recover from and continuously learn from them.
More than just a compliance exercise, DORA represents a fundamental shift towards resilience-by-design, embedding governance, risk management, testing, incident reporting and third-party oversight at the heart of financial organisations.
Contact our experts Astrid Wagner, Faustine Cachera and Bénédicte d’Allard for further assistance in understanding how DORA impacts your activities and the range of services we offer, from policy upgrade and contractual alignment to comprehensive reviews of your ICT risk management framework.
Produce your DORA register of information in one click
Coverage of the DORA report builder
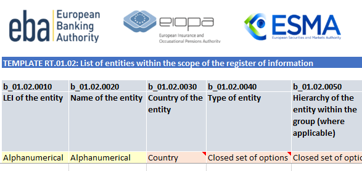
- Compliant with ESA ITS and RTS at all times, allowing financial entities to submit their register of information in accordance with applicable reporting deadlines
- With auditing functionalities
- Enriched with business data for enhanced use
Delivery model
- Simplified
- Centralised
- Automated
- Error-free
- Logic
One-click generation

- All CSV files in one folder
- Ready to be filed with the authorities
RegICT: use one platform with all your ICT regulatory controls
Regulatory ICT compliance is becoming a full-time exercise. Financial institutions face an ever-growing number of ICT-related obligations requiring periodic reviews, testing, evidence collection and management reporting. Coordinating these controls across business teams, IT functions and service providers can quickly become complex, time-consuming and difficult to track. A centralised and automated approach is key to maintaining compliance while reducing operational burden.
Key features of RegICT – our regulatory ICT control planner
- A comprehensive library of applicable regulatory ICT requirements and associated controls, customised to your regulatory profile.
- Centralised management of ICT requirements, controls and evidence collection activities.
- Automated delegation of tasks across multiple teams, e.g. ICT functions and service providers.
- User-friendly calendar dashboard to monitor and manage recurring regulatory controls.
- Streamlined collection of supporting documentation to stay audit-ready at all times.
Outsource your CISO function
Strengthen your cyber resilience with on-demand CISO expertise. We provide strategic cybersecurity leadership, regulatory guidance and robust ICT risk management to help your organisation stay secure, compliant and prepared for the evolving threat landscape.